Google Research Report Outlines Contextual Integrity for Agentic AI Privacy and Security
A new workshop report from Google details open challenges in building trustworthy autonomous agents using Contextual Integrity theory. The October 2025 workshop brought…
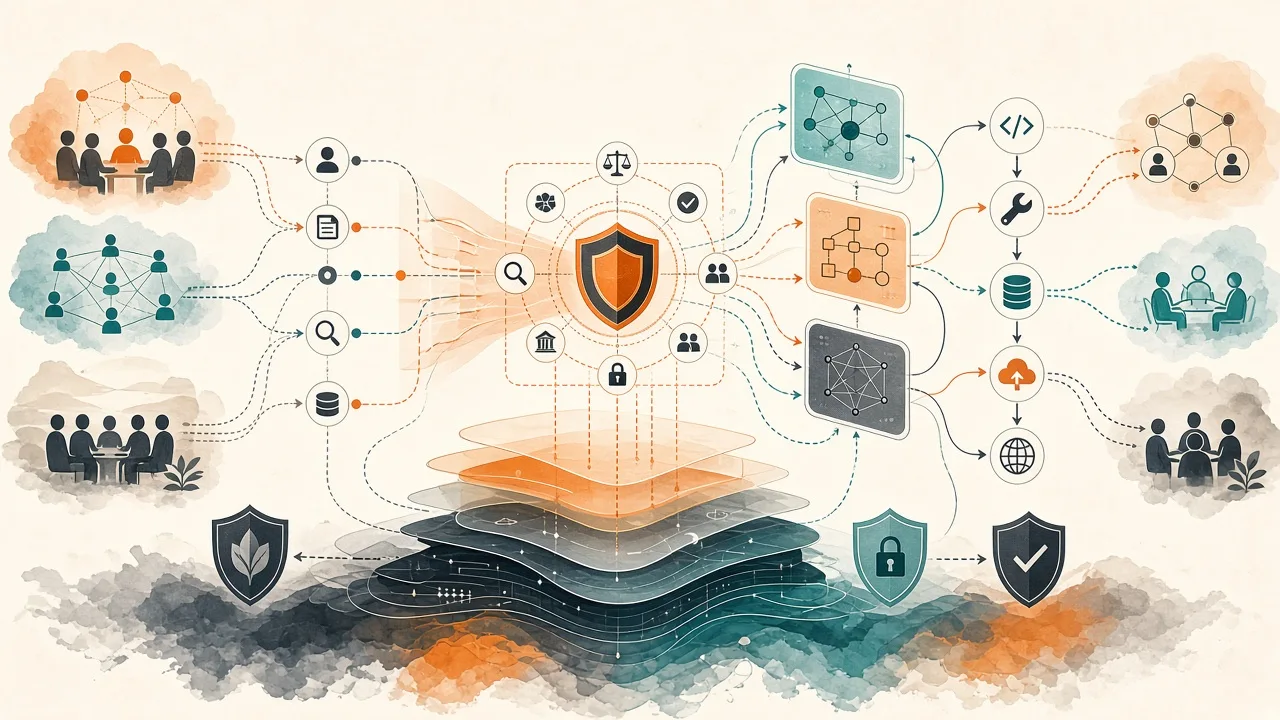
- Agentic systems require dynamic contextual policy engines to evaluate appropriateness of data flows and actions beyond static permissions.
- Traditional notice-and-choice privacy models are insufficient for probabilistic, autonomous agents that generate unpredictable execution paths.
- Standardized multi-agent simulation environments called Agent Gym are proposed to enable shared safety benchmarks across research groups.
Timeline of the Initiative
The Google Contextual Agent Privacy and Security (CAPS) Workshop took place in late 2025 in New York City. Over 50 academic and industry leaders from various institutions participated in discussions on agentic challenges.
On October 5, 2026, Google Research published the resulting workshop report titled Open and Emergent Problems in Agentic Privacy and Security: A Contextual Angle. The report, co-authored by more than 50 contributors, was led by primary authors including Lillian Tsai, Eugene Bagdasarian, and Marco Gruteser.
The publication calls for coordinated research across academia, government, civil society, and industry to develop contextual foundations for safe agentic AI.
Core Challenges of Agentic AI
The report identifies three critical dimensions that distinguish agents from traditional deterministic software: unstructured interfaces leading to input ambiguity and prompt injection risks, probabilistic control flows from generative planning, and increasing autonomy with delegation that reduces effective user oversight.
These factors create trade-offs where useful agents require broad access to personal data and the ability to take consequential actions, yet their behavioral flexibility demands new approaches to privacy and security.
The authors argue that agents must understand and be constrained by contextual behavioral norms to act appropriately in specific situations.
Contextual Integrity as the Foundation
Grounded in Helen Nissenbaum's theory of Contextual Integrity, the report defines privacy as appropriate information flow according to social norms rather than mere secrecy or user control. It generalizes this to contextual security for evaluating the appropriateness of agent actions.
Key elements include actors involved, types of information such as medical or financial data, and transmission principles like confidentiality. For instance, sharing a gift list with a shopping assistant may be appropriate while sharing it with family might not.
Large language models now offer the first opportunity to bridge the semantic gap between high-level norms and low-level system permissions through machine-readable, context-dependent policies.
Proposed Multi-Layered Solutions
The report advocates a contextual policy engine within a supervisor layer that dynamically generates and enforces policies in real time, evaluating actions before execution. This complements advances in model reasoning, user controls, and system sandboxing.
System-level innovations include dynamic sandboxing that adjusts capabilities based on changing contexts rather than static limits. Model-level work focuses on disambiguating prompts and reasoning about appropriateness under evolving norms.
User-centric designs shift from static notice-and-choice to dynamic, personalized interfaces. Additional areas cover multi-agent guardrails to prevent collusion and ecosystem governance for norm collection, conflict resolution, and compliance verification.
Evaluation and Call to Action
New dynamic safety evaluations are needed for autonomous multi-agent systems. The report proposes standardized open-source Agent Gym simulation environments to test cascading interactions and establish shared baselines for privacy, security, and safety.
This ambitious effort requires unprecedented collaboration. The publication serves as a call to the broader research community to advance contextual approaches for trustworthy agentic ecosystems.